- Product
- Sentinel
- Focus
- AI Security Engineering
- Audience
- AI product teams, security engineers and technical leaders introducing tool-using agents into business workflows.
- Evidence
- Working demo, source and tests
What this system solves
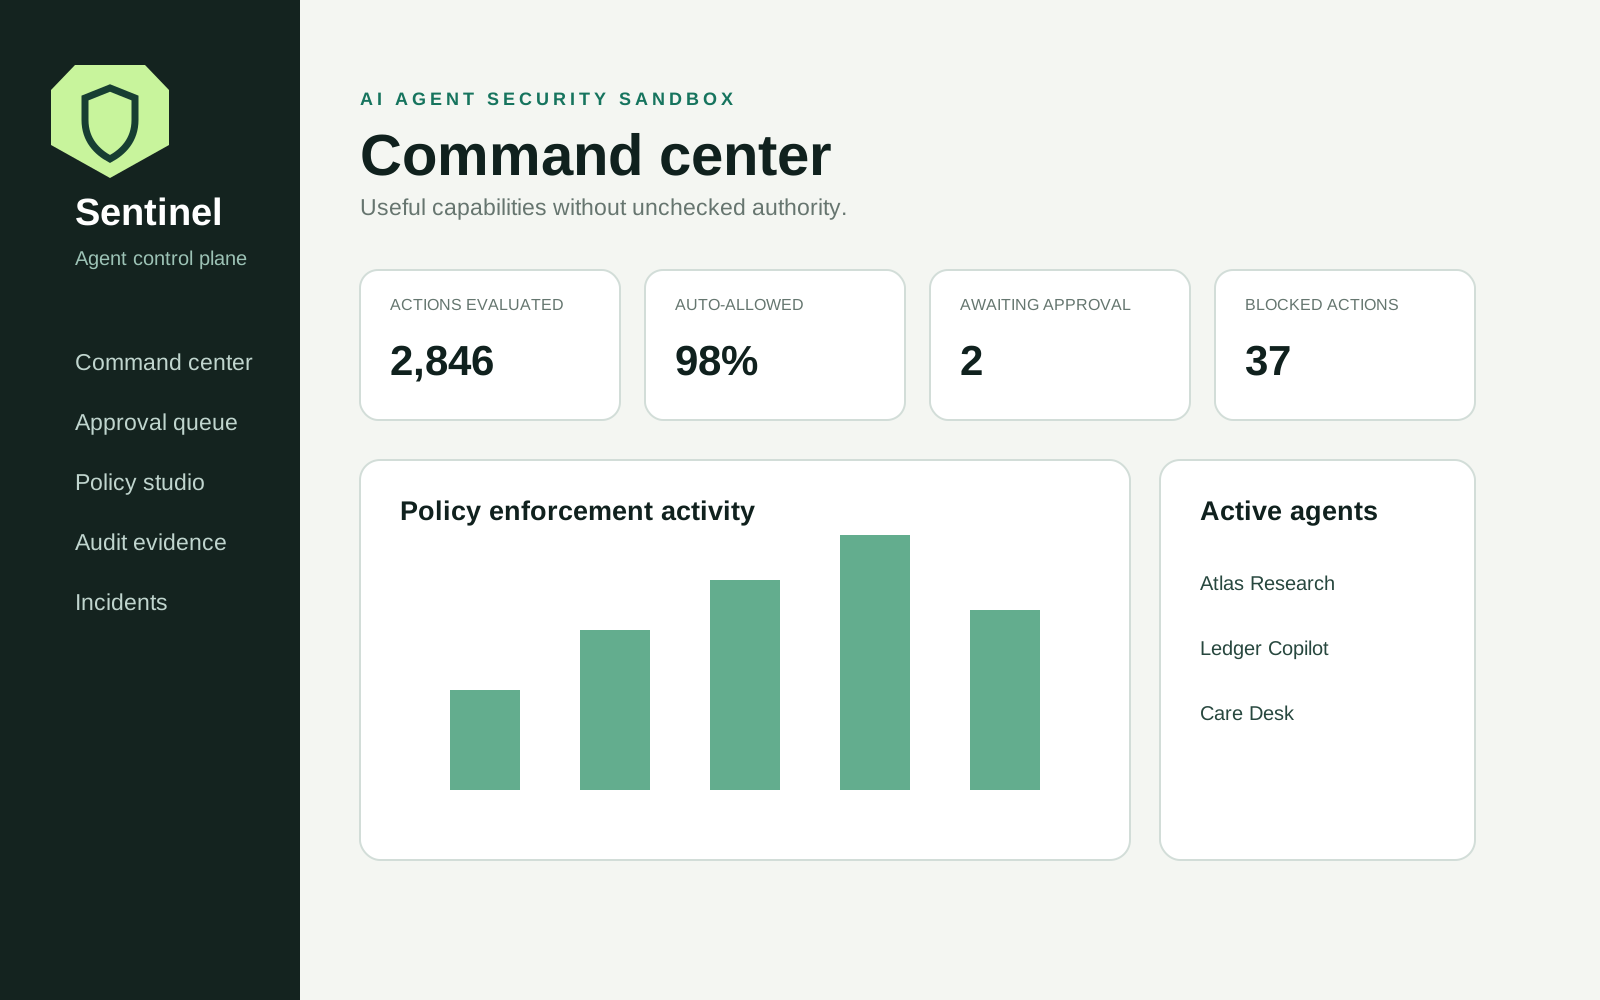
Sentinel demonstrates how an AI agent can receive useful capabilities without receiving unrestricted authority. Every proposed action is evaluated against identity, scope, data sensitivity, destination and risk before it is allowed, paused, blocked or contained.
AI product teams, security engineers and technical leaders introducing tool-using agents into business workflows.
My role
I designed the permission model, approval workflow, risk evaluation, containment scenarios, evidence trail and interactive control-plane interface.
Capabilities demonstrated
- Default-deny tool access
- Least-privilege permission scopes
- Human approval for sensitive actions
- One-use capability grants
- Prompt-injection containment
- Hash-linked audit evidence and incident recovery
System flow
Important decisions
An approval authorizes one reviewed capability, not unlimited access. Sensitive actions pause before execution, approvals expire after use, and hostile prompt signals revoke capabilities before investigation continues.
Beyond the happy path
The containment path revokes the active capability, blocks network egress, quarantines the session and preserves evidence. Restoration happens narrowly after review.
Testing and evidence
The repository contains 11 policy tests covering authorization, approval and containment behavior. All agents, records and security events in the browser are synthetic.
Current limitations
This controlled browser demonstration does not connect to external AI models, private production systems, real credentials or customer data.
Production extension path
A production control plane would add organization identity, signed policy versions, external model and tool adapters, secure credential brokering, durable audit storage and security-monitoring integrations.
Tools and concepts
Let’s work together
Building something that needs to work beyond the happy path?
I help teams turn complex product, integration and reliability requirements into clear, maintainable software.